The Dead-Config Problem
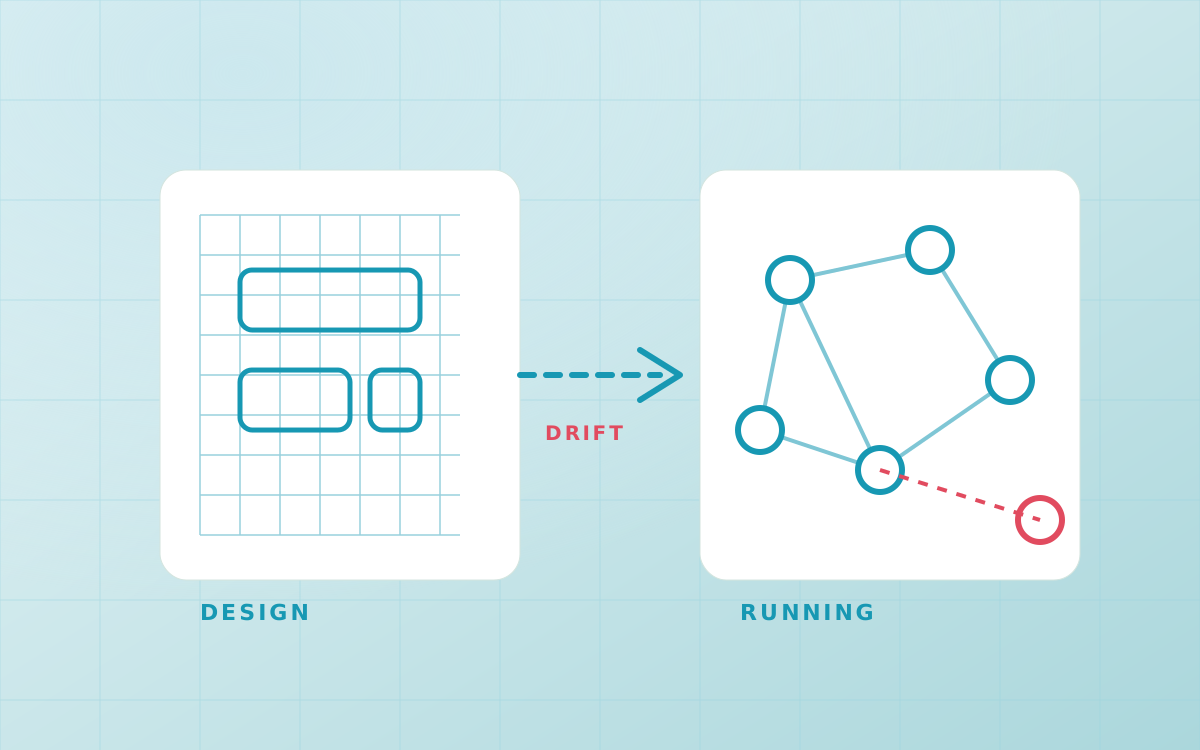
The dead configuration policies in production network is a major challenge for most IT networking group and security groups.
Companies spend millions of dollars on network security to make sure malicious user or DDoS attacks on company's resources & data. However, what they fail to address is, there is a big security risk with people who were granted access earlier due to valid business reasons but their access is not revoked once business engagement is terminated.
Example: Partner Connectivity with Enterprise Network
For example, "Partner Connectivity with Enterprise Network".
A medium to large size enterprise/financial institution works with various partners (solution partner, product partner, implementation partner, sales/marketing partners etc.). In order for these partners to work seamlessly with enterprise/financial businesses, partners users are given secured access to enterprise network. Typically, this process requires adding/changing network ACLs across enterprise network, apart from other steps.
Questions to Ask About Your Network
Do you see dead-network-acls in your network? How do you know what ACLs are applied for what purpose? How to clean ACLs once partner contract is terminated?
If you are interested to know how blaZop platform can help?
About blaZop
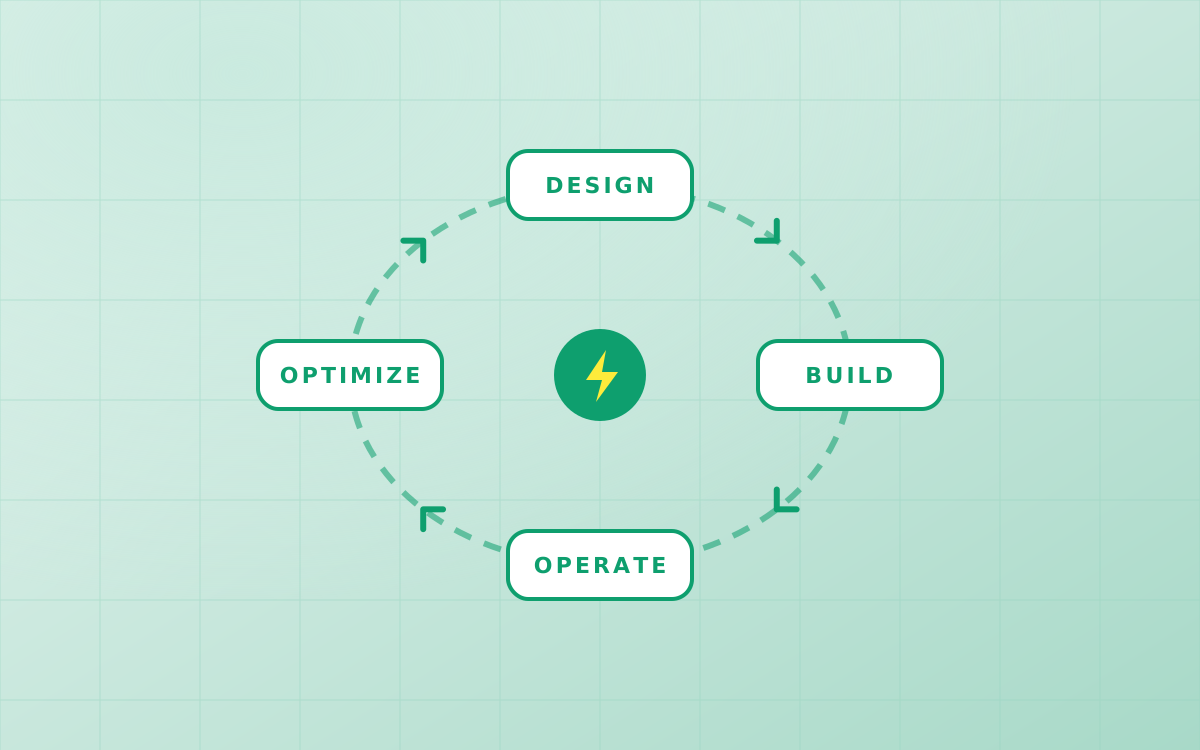
blaZop is an AI-powered hyper-automation & observability platform that enables autonomous IT and cloud operations. It empowers teams to achieve more with less effort, consolidate tools, reduce operational costs, establish and maintain more secure and standardized environments, minimize outages, and gain an insightful view of all IT and cloud services from a single interface. The unified platform includes a range of integrated products for managing the entire lifecycle (design, build, operate, and optimize) of multi-vendor & complex IT and cloud environments.
How a Valid ACL Becomes a Dead Config
What to remember
- Dead configuration policies in production networks are a major challenge for IT networking and security groups.
- Heavy spending on perimeter security does not address access granted for valid business reasons that is never revoked after the engagement ends.
- Partner connectivity (solution, product, implementation, sales/marketing partners) typically requires adding or changing network ACLs across the enterprise network.
- Once a partner contract is terminated, those ACLs often linger as dead-network-acls with no record of what they were applied for.
- Teams need a way to see which ACLs exist, why they were applied, and how to clean them up — the gap the blaZop platform addresses.